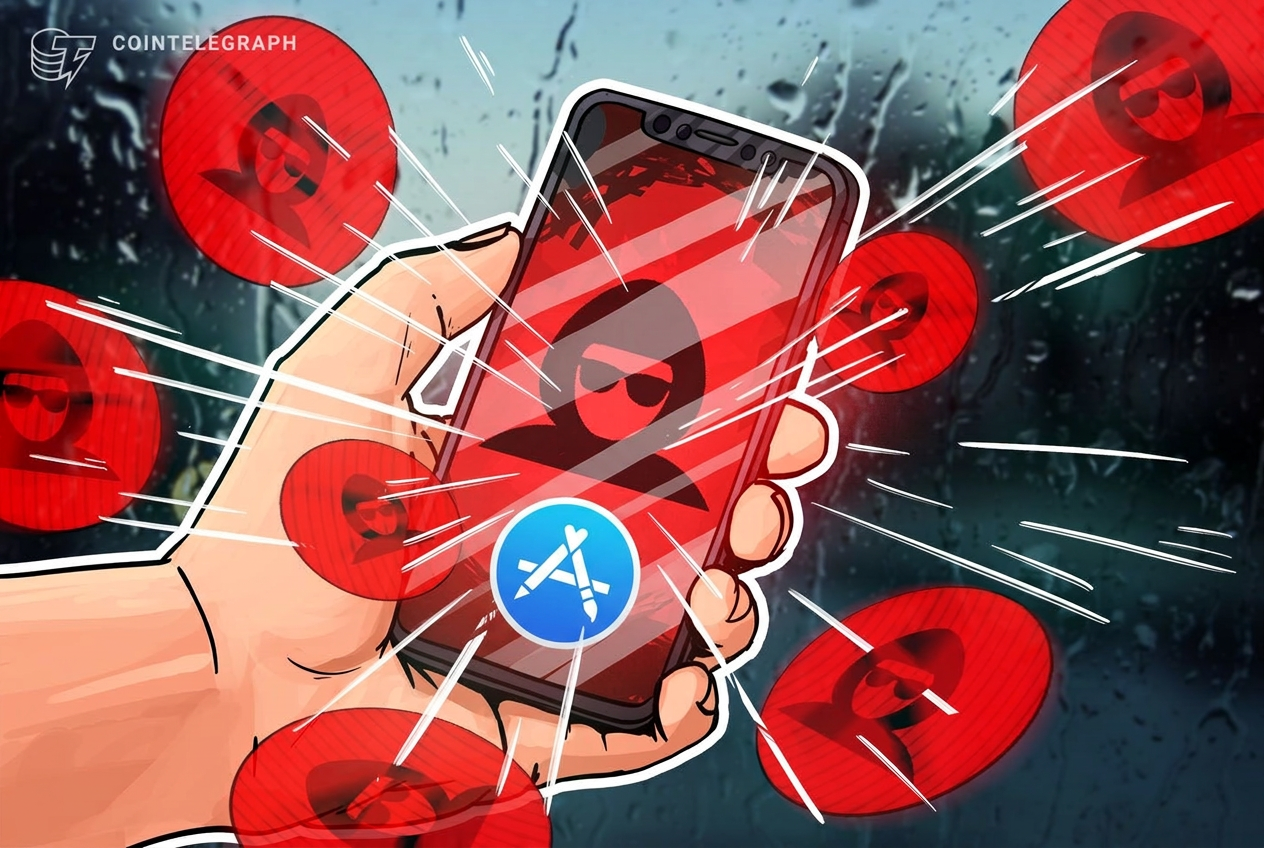
Malicious iOS app FomoPeek linked to $580K crypto theft, SlowMist says
Cointelegraph · 21 hr ago
$LINK
Informational impactNot rated
AI confidenceNot rated
Risk contextUnknownOperational, security or regulatory context
AI-ASSISTED
Verify with sourceFeed summary
SlowMist said malicious FomoPeek versions distributed through Apple’s App Store used iOS kernel exploits to escape the sandbox and access sensitive data from other apps.
AI output is based only on the stored feed text and may be incomplete or incorrect. It is not investment advice. Verify important claims at the original source.
KEEP EXPLORING
Related coverage
Security
An AI Agent Just Hacked a Government Website for the First Time, Australia PM Says
Decrypt · 4 hr ago
Security
OpenAI Gives Ukraine Access to Daybreak AI Cyber-Defense Tool
Decrypt · 4 hr ago
Security
Former Hack VC partner Hsin-Ju Chuang found dead at 37
Cointelegraph · 6 hr ago
Security
Former Hack VC partner Hsin-Ju Chuang found dead following public dispute with the firm
CoinDesk · 7 hr ago
Security
North Korea's Fake Job Interviews Drained $11M From 7,000 Crypto Wallets
Decrypt · 14 hr ago
Exchanges